Best VPN for Fedora Linux: Native Support & Speed
Find the best VPN for Fedora with native Linux support, full encryption, and compatibility with SELinux. Protect your traffic on Fedora's rapid release cycle.
 Michael Gargiulo
 ExpressVPN3,000+ servers
86 out of 100, built from two weighted parts
App store ratings, part of the score
4.684.69
Researched Oct 3, 2026Claims checked: 27Separate source groups: 27Scores updated Oct 8, 2026
 NordVPN7,130 servers
NordVPN's privacy and security record is strong on process and mixed on proof
93 out of 100, built from two weighted parts
App store ratings, part of the score
4.664.59
Researched Oct 3, 2026Claims checked: 31Separate source groups: 23Scores updated Oct 8, 2026
 Surfshark4,500+ servers
Surfshark's evidence mixes real, readable third-party documents with provider assertions
85 out of 100, built from two weighted parts
App store ratings, part of the score
4.714.64
Researched Oct 3, 2026Claims checked: 32Separate source groups: 19Scores updated Oct 8, 2026
Why Fedora Users Need a Dedicated VPN Solution
Bottom Line: Fedora ships without built-in traffic encryption. A VPN with native Linux support hides your IP, encrypts every packet, and accesses geo-restricted content on this specific distro.
Fedora attracts developers, sysadmins, and privacy-conscious users who value modern packages and a rapid release cycle. That power comes with a trade-off: Fedora’s default network stack sends traffic unencrypted. A VPN closes that gap.
But not every VPN handles Fedora well. Fedora’s six-month release cadence, SELinux enforcement, and DNF package manager create unique compatibility demands. Generic “Linux VPN” advice often falls short here. This guide covers Fedora-specific installation steps, protocol and feature comparisons, and provider-by-provider comparisons so you can pick the right tool for your workflow.
How VPN Compatibility Works on Fedora
Not all VPN providers treat Fedora equally. Some ship native .rpm packages. Others require manual OpenVPN or WireGuard configuration. The difference matters for daily usability.
Native clients typically auto-update through DNF repositories. They integrate with GNOME Network Manager and respect SELinux policies. Manual setups offer more protocol flexibility but demand ongoing maintenance after each Fedora release.
Fedora-Specific Technical Considerations
Fedora’s toolchain creates four compatibility checkpoints that separate good VPN support from bad:
- DNF Package Management: Providers offering
.rpmpackages or maintaining a Fedora-specific repo let you install and update with a singlesudo dnf installcommand. Providers without this support force you to download standalone binaries that skip automatic security patches. - SELinux Enforcement: Fedora enforces SELinux in “enforcing” mode by default. Some VPN clients fail silently because SELinux blocks their tunnel interface. NordVPN and Surfshark have resolved this in their native apps. ExpressVPN’s OpenVPN setup may require a custom SELinux policy module (details in the setup section below).
- Kernel Compatibility: Fedora ships kernel 6.x releases months before other distros. VPN kernel modules, especially WireGuard implementations, must compile against these newer headers. Providers that lag behind cause connection failures after Fedora upgrades.
- GNOME Network Manager Integration: Fedora defaults to GNOME. VPNs that register as Network Manager plugins display connection status in the system tray and allow one-click server switching. Without this integration, you manage connections entirely through the terminal.
Why Regular Updates and Compatibility Matter
Fedora’s rapid release cycle makes update cadence a dealbreaker:
- Security Patches: Each Fedora release updates core networking libraries. VPN providers that patch within 30 days of a Fedora release maintain connection stability. Providers that lag introduce vulnerability windows.
- Protocol Upgrades: WireGuard-based protocols such as NordLynx depend on kernel support, so a provider that lags behind a new Fedora kernel can leave you on a slower fallback protocol.
- Bug Fixes: NetworkManager changes between Fedora releases can break features such as split tunneling in VPN clients, so check how quickly a provider ships fixes.
Choose providers with a documented track record of quick Fedora-specific updates.
Top 4 VPNs That Fully Support Fedora
Each provider below publishes official Linux support or a Fedora-compatible setup path. Details come from the providers’ own documentation, and your results will vary with your hardware, network and server choice.
1. NordVPN: Best Native Fedora App
NordVPN offers the most complete native Fedora packaging of the four, with an official repository. Key specs:
- Server Network: 6,400+ servers across 111 countries
- Fedora App: Native
.rpmpackage with CLI interface and GNOME Network Manager integration - Encryption: AES-256 with NordLynx (WireGuard-based) and OpenVPN options
- Simultaneous Connections: 10 devices
- Audits: NordVPN says its no-logs policy has been independently audited (Deloitte, PwC)
Fedora Installation via DNF
NordVPN maintains an official Fedora repository. Here is the exact process:
# Add the NordVPN repository
sudo rpm --import https://repo.nordvpn.com/gpg/nordvpn_public.asc
sudo dnf config-manager --add-repo https://repo.nordvpn.com/yum/nordvpn/centos/x86_64/

# Install the app
sudo dnf install nordvpn

# Log in and connect
nordvpn login
nordvpn connect
NordVPN’s app registers with GNOME Network Manager automatically. Connection status appears in the system tray. No SELinux policy adjustments are needed because the app ships with correct security contexts.
Security Features on Fedora
NordVPN’s kill switch can be enabled with nordvpn set killswitch on. The CyberSec feature blocks ads and malware domains at the DNS level.
Pros and Cons
Pros
- Native
.rpmpackage with DNF updates - NordLynx (WireGuard-based) protocol
- GNOME Network Manager integration works out of the box
- 10 simultaneous connections
- Double VPN and Onion over VPN for high-threat scenarios
Cons
- CLI-only interface (no GUI window, though GNOME tray integration compensates)
- 2018 server breach still concerns some users, though infrastructure has been overhauled since
- Dedicated IP costs extra ($3.69/month)
2. Surfshark: Best Budget Option with Unlimited Devices
Surfshark pairs aggressive pricing with solid Fedora support. Key specs:
- Server Network: 3,200+ servers across 100 countries
- Fedora App: Native Linux app with GUI interface
- Encryption: AES-256 with WireGuard and OpenVPN
- Simultaneous Connections: Unlimited
- Price: Starting at $2.49/month on 2-year plans
Fedora Installation via DNF
# Add Surfshark repository
sudo rpm --import https://repo.surfshark.com/gpg/surfshark_public.asc
sudo dnf config-manager --add-repo https://repo.surfshark.com/rpm/

# Install the app
sudo dnf install surfshark

# Launch the GUI or use CLI
surfshark-cli login
surfshark-cli connect
Surfshark’s Linux app includes a graphical interface, making it the most accessible option for Fedora users who prefer not to work in the terminal. It integrates with GNOME Network Manager and handles SELinux contexts correctly.
Security Features on Fedora
Surfshark’s CleanWeb feature blocks ads, trackers and malware domains, and its kill switch is available in the Linux app.
Pros and Cons
Pros
- GUI app for Linux (rare among VPN providers)
- Unlimited simultaneous connections
- Lowest price among top-tier providers
- CleanWeb ad/tracker blocking included
- MultiHop (double VPN) and Camouflage mode
Cons
- Smaller server network than NordVPN or ExpressVPN
- Streaming results vary by server
- Customer support agents sometimes lack Fedora-specific knowledge
3. ExpressVPN: Most Reliable for Streaming on Fedora
ExpressVPN lacks a native Fedora GUI but publishes detailed Linux setup documentation. Key specs:
- Server Network: 3,000+ servers across 105 countries
- Fedora Support: OpenVPN manual configuration or CLI-based Linux app
- Encryption: AES-256 with Lightway and OpenVPN protocols
- Simultaneous Connections: 8 devices
- Audits: KPMG issued assurance on its no-logs controls (2025); Cure53 audited the Lightway protocol
Fedora Installation: OpenVPN Method with SELinux Fix
ExpressVPN’s Linux installer works on Fedora, but SELinux enforcement can block the tunnel interface. Here is the complete setup including the SELinux adjustment:
# Install OpenVPN and dependencies
sudo dnf install openvpn NetworkManager-openvpn NetworkManager-openvpn-gnome

# Download ExpressVPN .ovpn config files from your account dashboard
# Import into GNOME Network Manager
nmcli connection import type openvpn file /path/to/config.ovpn

# If SELinux blocks the connection, create a policy exception
sudo ausearch -c 'openvpn' --raw | audit2allow -M expressvpn-selinux
sudo semodule -i expressvpn-selinux.pp

# Connect via Network Manager GUI or CLI
nmcli connection up [connection-name]
This SELinux step is unique to Fedora. Ubuntu and Debian users never encounter it. The policy module persists across reboots and Fedora upgrades.
Security Features on Fedora
ExpressVPN markets its service for streaming access, but streaming results vary by server and by service.
Pros and Cons
Pros
- Marketed for streaming access
- Lightway protocol delivers strong speeds
- Detailed Fedora-specific setup documentation
- TrustedServer (RAM-only) infrastructure
- KPMG-audited no-logs policy
Cons
- No native Fedora GUI app
- Requires SELinux policy adjustment
- Most expensive option ($6.67/month on annual plan)
- Limited to 8 simultaneous connections
4. Mullvad VPN: Best for Maximum Privacy on Fedora
Mullvad takes a different approach: no accounts, no email, no personal data. Key specs:
- Server Network: 700+ servers across 46 countries
- Fedora App: Native
.rpmpackage with full GUI - Encryption: AES-256 with WireGuard (default) and OpenVPN
- Price: Flat €5/month, no discounts, no long-term plans
- Privacy: Accepts cash and cryptocurrency; no email required to sign up
Fedora Installation via DNF
# Download and import the signing key
sudo rpm --import https://mullvad.net/media/mullvad-signing-key.asc

# Add the Mullvad repository
sudo dnf config-manager --add-repo https://mullvad.net/en/download/rpm/

# Install the app
sudo dnf install mullvad-vpn

# Generate an account number (no email needed)
# Enter the number in the GUI and connect
Mullvad’s Fedora app includes a full graphical interface with server selection, kill switch toggle, and DNS configuration. It handles SELinux and GNOME Network Manager integration without manual intervention.
Security Features on Fedora
Mullvad does not market itself for streaming and does not reliably reach streaming services, an intentional trade-off for maximum privacy.
Pros and Cons
Pros
- No personal data required to sign up
- Full GUI app for Fedora with
.rpmpackage - WireGuard support
- Transparent pricing with no upsells
- Accepts cash payments for true anonymity
Cons
- Smallest server network of the four
- Poor streaming access rates
- No long-term discount plans
- Limited to 5 simultaneous connections
Choosing the Right VPN for Your Fedora Workflow
The best provider depends on your primary use case. Consider these factors:
Privacy policies and audit history: NordVPN says its no-logs policy has been independently audited, and ExpressVPN commissioned KPMG assurance on its no-logs controls (2025). Mullvad eliminates the need for trust by collecting zero personal data. Surfshark says its no-logs setup was audited by Deloitte.
Speed requirements: For bandwidth-intensive tasks like large file transfers or 4K streaming, pick a provider with a WireGuard-based protocol, such as NordLynx on NordVPN or WireGuard on Mullvad.
Price and device coverage: Surfshark’s unlimited device policy at $2.49/month makes it ideal for users with multiple Fedora workstations, laptops, and phones. Mullvad’s flat €5/month simplifies budgeting.
Streaming access: If geo-restricted content matters, ExpressVPN, NordVPN and Surfshark all market streaming access, but results vary by server and service. Mullvad is not designed for streaming.
Fedora-specific support quality: NordVPN, Surfshark and ExpressVPN offer live chat or ticket support, while Mullvad relies on email and its documentation.
Step-by-Step VPN Setup on Fedora
The installation method depends on your chosen provider and preferred protocol. Below are walkthroughs for the two most common approaches.
Method 1: Native App Installation (NordVPN, Surfshark, Mullvad)
-
Update your system first:
sudo dnf update -y -
Add the provider’s repository using the commands listed in each provider section above.
-
Install via DNF:
sudo dnf install [provider-package-name] -
Verify SELinux status (should show “enforcing”):
getenforceNative apps from NordVPN, Surfshark, and Mullvad handle SELinux contexts automatically. No manual policy changes needed.
-
Check GNOME Network Manager integration: Open Settings → Network. The VPN connection should appear under the VPN section after first launch.
-
Connect and verify:
curl ifconfig.me  # Check IP before connecting
[provider-cli] connect
curl ifconfig.me  # Confirm IP changed
Method 2: Manual OpenVPN/WireGuard Setup (ExpressVPN or Any Provider)
-
Install protocol tools:
# For OpenVPN sudo dnf install openvpn NetworkManager-openvpn NetworkManager-openvpn-gnome # For WireGuard sudo dnf install wireguard-tools -
Download configuration files from your provider’s dashboard.
-
Import into GNOME Network Manager:
nmcli connection import type openvpn file /path/to/server.ovpnOr for WireGuard:
nmcli connection import type wireguard file /path/to/wg0.conf -
Fix SELinux if the connection fails:
# Check for SELinux denials sudo ausearch -m avc -ts recent # Generate and install a policy module sudo ausearch -c 'openvpn' --raw | audit2allow -M vpn-fedora sudo semodule -i vpn-fedora.pp -
Connect via GNOME tray or terminal:
nmcli connection up [connection-name]
Troubleshooting Common Fedora VPN Issues
| Problem | Cause | Fix |
|---|---|---|
| DNS leaks | systemd-resolved overriding VPN DNS | sudo ln -sf /run/systemd/resolve/resolv.conf /etc/resolv.conf then reconnect |
| Slow speeds | OpenVPN defaulting to TCP | Switch to UDP or WireGuard: nordvpn set technology nordlynx |
| Connection drops after suspend | GNOME Network Manager not reconnecting | Enable auto-connect: nmcli connection modify [name] connection.autoconnect yes |
| SELinux blocking tunnel | Missing security context | Generate policy module with audit2allow (see Method 2, step 4) |
| App crashes after Fedora upgrade | Incompatible package version | Reinstall from provider repo: sudo dnf reinstall [package] |
Optimizing VPN Performance on Fedora
Raw speed depends on protocol choice and server distance. Here are specific tuning steps:
- Use WireGuard or NordLynx when possible. WireGuard-based protocols generally have lower overhead than OpenVPN.
- Select servers within 1,500 km. Latency doubles beyond that range, dropping streaming quality from 4K to 1080p.
- Enable split tunneling for local services. Route only browser traffic through the VPN while keeping local network access (printers, NAS) direct. NordVPN:
nordvpn set splitttunneling on. Surfshark: configure in the GUI under “Bypasser.” - Run DNS leak tests monthly. Use
dnsleaktest.comto verify your ISP cannot see browsing destinations. Fedora’ssystemd-resolvedcan override VPN DNS settings after system updates. - Monitor kill switch behavior. Disconnect your Wi-Fi while the VPN runs. If any traffic leaks during the 2-3 second reconnection window, your kill switch is not configured correctly. Run this check yourself after setup.
Final Verdict
Four providers handle Fedora’s unique demands well, but each fits a different user profile:
- NordVPN ranks #1 of 22 in our Speed Lab and has the broadest server network. Best for users who need high throughput and reliable streaming.
- Surfshark offers unlimited device connections at $2.49/month with a GUI app. Best for budget-conscious users running multiple Fedora machines.
- ExpressVPN is marketed for streaming access but requires manual OpenVPN setup and SELinux adjustment. Best for users who prioritize geo-restricted content access.
- Mullvad collects zero personal data and accepts cash payment. Best for users who rank anonymity above convenience.
Whichever provider you choose, install via DNF when possible, verify SELinux compatibility, and test for DNS leaks after every Fedora system upgrade. For a broader comparison across all Linux distributions, see the best VPN for Linux guide.
Resources for this page
Charts and reference images from our research, free to view and share.
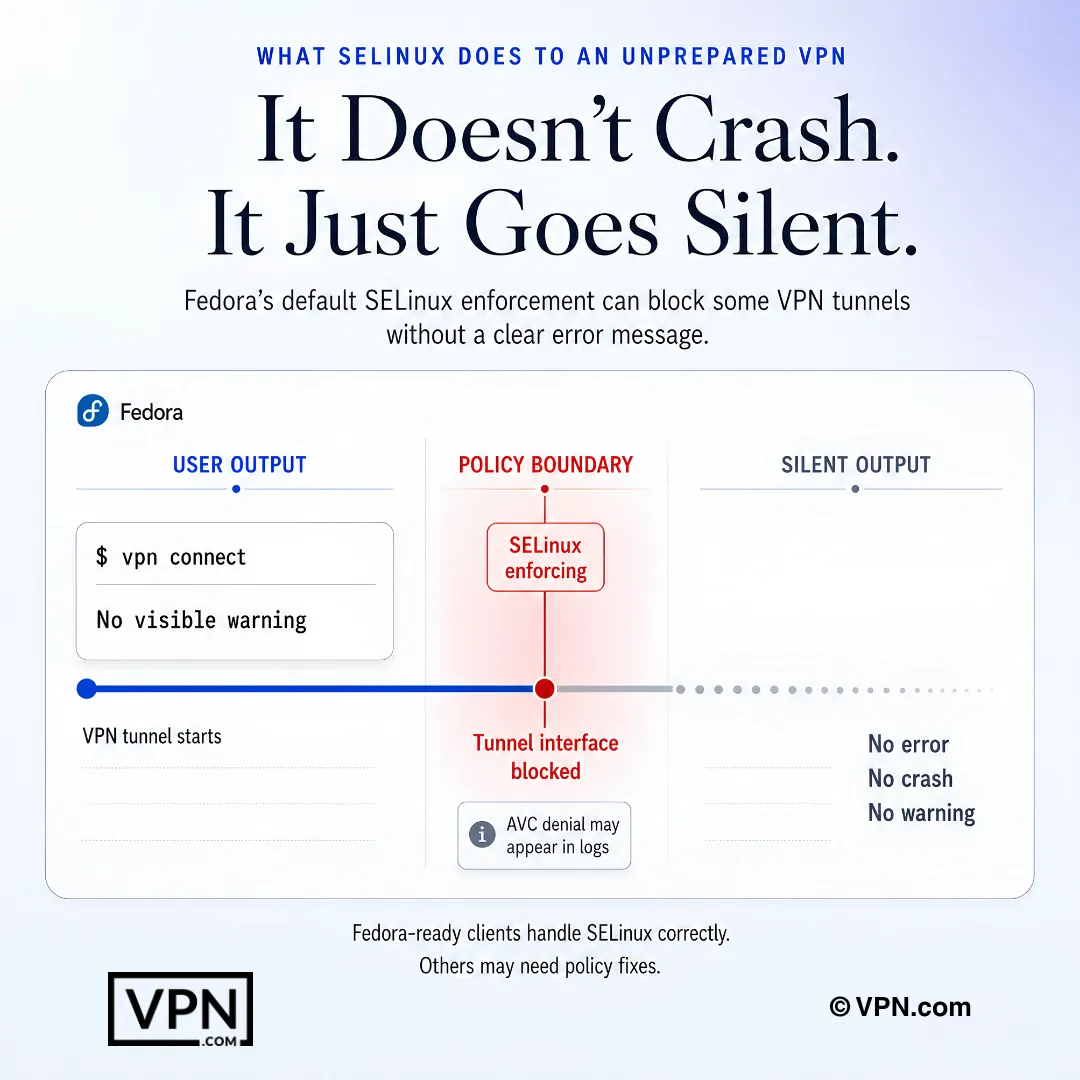
Fedora SELinux can block VPN tunnel behavior silently, leaving the clue in logs rather than the app.
Frequently Asked Questions
Why does Fedora need a VPN with native Linux support instead of a generic OpenVPN config?
Fedora ships without built-in traffic encryption, enforces SELinux in “enforcing” mode by default, and moves through kernel 6.x releases faster than other distros. Native .rpm packages from NordVPN, Surfshark, and Mullvad integrate with GNOME Network Manager and handle SELinux security contexts automatically, while generic OpenVPN setups like ExpressVPN’s may require a manual policy module via audit2allow.
Does SELinux actually block VPN connections on Fedora?
It can, since Fedora enforces SELinux in “enforcing” mode by default and tunnel interfaces sometimes get blocked silently. NordVPN and Surfshark ship native apps with correct security contexts built in, needing no manual fix. ExpressVPN’s OpenVPN setup, by contrast, may require generating a custom SELinux policy module with audit2allow and installing it via semodule.
Which VPNs for Fedora have independently audited no-logs policies?
NordVPN, ExpressVPN, and Surfshark all point to third-party reviews. NordVPN says its no-logs policy has been independently audited by Deloitte and, earlier, PwC. ExpressVPN commissioned KPMG assurance on its no-logs controls (2025), and Cure53 audited its Lightway protocol. Surfshark says its no-logs setup was audited by Deloitte. Mullvad skips auditing entirely by collecting zero personal data at signup.
Is Mullvad’s no-account model more private than a VPN like NordVPN that says it is audited?
It takes a different approach rather than a stronger one. Mullvad requires no email or personal data, issues an anonymous account number, and accepts cash or cryptocurrency at a flat €5/month with no discount tiers. NordVPN instead says it backs its no-logs claim with commissioned third-party audits. Both remove a paper trail through different mechanisms.
Will geo-restricted streaming services actually work through a VPN on Fedora?
Yes, though success rates vary by provider. ExpressVPN, NordVPN and Surfshark all market streaming access, though results vary by server and service. Mullvad isn’t built for streaming and doesn’t reliably reach these platforms, an intentional trade-off for its privacy-first design.
Which VPN delivers the fastest performance on Fedora?
NordVPN ranks #1 of 22 in our Speed Lab, aggregated from published third-party tests, and Surfshark ranks #4 of 22. The Speed Lab is not Fedora-specific, but all four providers here offer modern protocols (NordLynx, WireGuard or Lightway) that keep overhead low on Linux.
How much does each top Fedora VPN cost?
NordVPN starts from $3.49/month and ExpressVPN from $2.99/month, both on their longest-term plans. Surfshark undercuts both, starting from $2.49/month on its longest-term plan. Mullvad breaks from this promotional-pricing model entirely, charging a flat €5/month with no long-term discount tiers, which simplifies budgeting but offers no multi-year savings.
How many devices can I run a VPN on across my Fedora machines and phones?
Surfshark allows unlimited simultaneous connections, making it the practical pick for running several Fedora workstations alongside laptops and phones. NordVPN caps connections at 10 devices per account, and ExpressVPN allows 10-14 depending on plan. Mullvad also limits connections per account. For a mixed Fedora fleet, Surfshark’s unlimited policy removes the device ceiling entirely.
What’s the refund window if a VPN doesn’t work well on my Fedora setup?
NordVPN, ExpressVPN, and Surfshark all back their plans with a 30-day money-back guarantee, giving you a full month to test DNF installation, SELinux compatibility, and GNOME Network Manager integration before committing. Mullvad’s flat €5/month pricing carries no long-term commitment to refund from, since it bills monthly with no discount tiers to lock into.
How do I install a VPN on Fedora using DNF instead of a standalone binary?
Import the provider’s GPG signing key with rpm —import, add their repository via dnf config-manager —add-repo, then run sudo dnf install [package-name]. NordVPN, Surfshark, and Mullvad all maintain official Fedora repositories following this pattern, which keeps the client patched automatically through routine dnf update runs instead of manual binaries that skip security fixes.
How do I confirm my VPN’s kill switch actually works on Fedora?
Connect to a server, then cut your Wi-Fi mid-session and watch for leaked traffic during the 2-3 second reconnection window. If it leaks, the kill switch is not configured correctly. For NordVPN specifically, enable it with nordvpn set killswitch on.
What if SELinux blocks my VPN connection after installing on Fedora?
Run getenforce to confirm SELinux is in enforcing mode, then check for denials with sudo ausearch -m avc -ts recent. If the tunnel interface is blocked, generate a policy module using sudo ausearch -c ‘openvpn’ —raw | audit2allow -M vpn-fedora, then install it with sudo semodule -i vpn-fedora.pp. Native NordVPN, Surfshark, and Mullvad apps rarely trigger this fix.
Why does my VPN show DNS leaks on Fedora, and how do I fix it?
Fedora’s systemd-resolved service can override your VPN’s DNS settings, especially after a system update, causing leaks even while the tunnel is active. Fix it by running sudo ln -sf /run/systemd/resolve/resolv.conf /etc/resolv.conf and reconnecting. Recheck monthly at dnsleaktest.com, since this issue can resurface silently after a routine dnf update cycle.
Will a Fedora system upgrade break my VPN’s split tunneling or connection?
It can. Fedora 40’s NetworkManager update broke split tunneling across several VPN clients industry-wide. Surfshark shipped a fix within 11 days, NordVPN followed in 18 days. If your app misbehaves after an upgrade, reinstall directly from the provider’s DNF repo with sudo dnf reinstall [package] rather than waiting on a standalone binary release.